ClearSkies begins its activity in the Spanish market with ClearSkies iISOC, its intelligent and integrated security operations platform (Intelligent-Integrated Security Operations Centre). ClearSkies iISOC brings together detection, investigation, response, automation and security intelligence capabilities in a single environment, with the goal of eliminating the fragmentation of managing cybersecurity operations through multiple disconnected tools.
One of the main meeting points of ClearSkies with the Spanish market will be Barcelona Cybersecurity Congress (BCC26), which will be held from November 3 to 5, 2026 at Fira Barcelona Gran Via. ClearSkies will participate as a Diamond Sponsor and will have its own stand (hall 2, stand A1), where it will demonstrate the platform and hold meetings, interviews and encounters with analysts and professionals in the sector.
A platform to integrate security operations
ClearSkies responds to a common reality in security teams: the need to work with multiple tools to monitor the different layers of an organization, detect threats, investigate incidents and execute response actions.
Faced with this fragmented model, ClearSkies’ iISOC approach combines two elements: intelligence and integration. On the one hand, it incorporates a layer of artificial intelligence that analyzes and contextualizes security information, helps identify relevant signals and prioritizes risks. On the other hand, the different capabilities of the platform work on the same data model, workflow and console.
The goal is for different security functions to work in a coordinated manner, reducing the need for analysts to manually collect and correlate information from different systems.
According to the most recent ClearSkies metrics, this approach reduces false positives by 95% and time spent on investigation by 80%, in addition to increasing analyst productivity by 48%, with a detection time of less than 30 seconds.
“For years, the cybersecurity industry has responded to increasingly sophisticated threats by adding more tools, more alerts and more complexity. We didn’t create ClearSkies iISOC to become just another tool in an already fragmented security stack; we created it to provide the intelligence that unifies technologies, people and processes into a single coordinated security operation,” said Eleftherios Antoniades, founder and CEO of Odyssey Cybersecurity and chief architect of ClearSkies.
“By combining generative and agentic AI with advanced threat detection, contextual intelligence and intelligent orchestration, ClearSkies™ iISOC transforms fragmented security data into actionable intelligence. It continuously correlates signals, builds complete context around threats, prioritizes risks and autonomously conducts investigations and orchestrates response flows within defined operational boundaries. Instead of overwhelming analysts with isolated alerts, it delivers contextualized incidents, evidence-based conclusions and actions Our vision is not simply to make security operations faster, but to fundamentally transform the way they operate, allowing AI to manage operational complexity while security professionals retain oversight, strategic control and accountability. This is the foundation of Autonomous SOC,” concludes Antoniades.
Generative and Agentic AI to move towards a more autonomous SOC
In an increasingly complex and larger-scale threat landscape, intelligent automation has become a key ally for security operations centers (SOC). To respond to this challenge, ClearSkies natively integrates Generative and Agentic artificial intelligence into its architecture, with the goal of transforming the way organizations analyze, investigate and neutralize incidents.
Generative AI transforms large volumes of data into understandable context, clear explanations and concrete recommendations that speed up the analytical work of security teams. For its part, Agentic AI automates critical workflows, such as initial triage, evidence collection, forensic investigation and certain response actions, always within the control limits established by each organization.
In this way, the platform drives a gradual transition towards more autonomous operations, maintaining human supervision as a central element. Automation is deployed through progressive levels of autonomy and customized policies, so that artificial intelligence not only interprets information, but can also perform some of the technical work necessary to protect corporate environments.
A common platform for different security areas
Traditionally, the evolution of security operations centers has been linked to the incorporation of independent tools to cover different needs: from security information and event management (SIEM) and orchestration, automation and response (SOAR) to threat intelligence, identity protection, endpoints and network control. This operational fragmentation can create inefficiencies and blind spots.
To overcome this dynamic, the ClearSkies architecture unifies these disciplines into an integrated environment. The platform combines SIEM, threat detection, investigation and response (TDIR), SOAR, threat intelligence, exposure management, identity security and AI-assisted investigation capabilities. All of this is connected through an AI-based orchestration layer that correlates data, prioritizes threats, and automates responses throughout the entire security cycle.
ClearSkies can work with the tools that organizations already use, so its adoption does not necessarily mean replacing existing investments. Additionally, organizations can extend specific capabilities through native add-ons such as ClearSkies ASM, for continuous management of the external attack surface, and ClearSkies™ DNS Shield, for protection at the DNS layer.
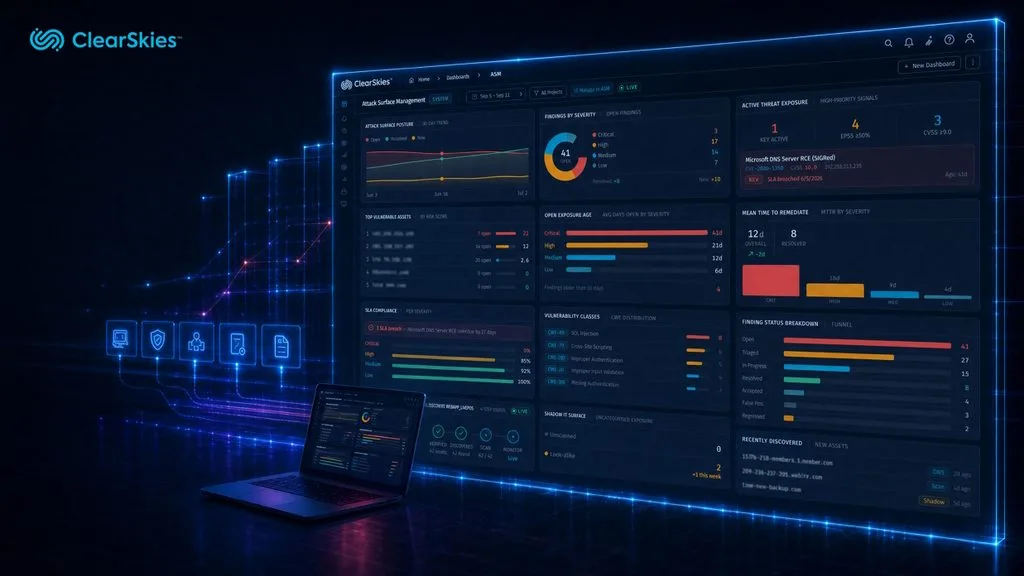
Both solutions are also available as stand-alone products and, when deployed alongside the platform, directly incorporate their results into the integrated environment. This way, organizations can start with a specific capability and progressively expand its use without having to migrate to a new platform.
Through December 31, 2026, ClearSkies ASM and ClearSkies DNS Shield annual plans include three additional months at no cost and a 15-day free trial.
Sovereignty and control at the center of the strategy
Along with the challenge of integration, the widespread adoption of artificial intelligence in corporate environments raises important questions about the privacy and sovereignty of sensitive data. To respond to security and regulatory compliance demands, including the cybersecurity requirements established by the European NIS2 directive, ClearSkies incorporates its Centric-AI Fabric technology.
The platform offers the flexibility to expand advanced cybersecurity services
This artificial intelligence architecture is designed to work with private and offline AI models. In this way, organizations can take advantage of the capabilities of automated analysis and advanced algorithms without compromising the confidentiality of their information or necessarily having to hand over control of the data to external infrastructures.
The platform offers different deployment modalities, from cloud environments to local infrastructures (on-premise) and hybrid models adapted to the restrictions of each organization. Its approach is based on a premise: although automation and artificial intelligence allow for increased operational autonomy, supervision, strategic decisions and limits of action must remain under the control of human teams.
ClearSkies expands its presence to the Spanish market with a proposal aimed at both companies and managed security service providers (MSSP), with the aim of developing a local distribution and collaboration network.
The company is establishing a business development structure in Spain and plans to promote a program for distributors and resellers as the basis of its commercial expansion in 2027.
Thanks to an architecture designed for both large enterprises that directly manage their defenses and MSSPs that operate in complex environments with multiple clients, the platform offers the flexibility necessary to expand advanced cybersecurity services. This strategy seeks to create a proximity ecosystem in Spain, in collaboration with local technology partners, to promote the adoption of the platform.